What Evidence of AI Involvement Can Establish
Confirmed AI involvement settles less than it seems. What detector scores, provenance records, and watermarks can and cannot establish about a work.
Read Full ArticleExplore our latest thoughts on AI governance, safety, and deterministic systems
Confirmed AI involvement settles less than it seems. What detector scores, provenance records, and watermarks can and cannot establish about a work.
Read Full Article
Adding rules, ontologies, solvers, or signed logs to IAM leaves an authorization gap intact if the deficient dependency is untouched. What must change instead.
Read Full Article
Containment restricts where a system can reach. Successful containment does not establish that the actions it permits are authorized. What a perimeter alone leaves open, and what authorization requires.
Read Full Article
Two systems can share the deterministic authorization label and differ in what they evaluate, enforce, and prove. What the claim leaves out, and who is expected to supply it.
Read Full Article
Behavioral monitoring can inform authorization but cannot replace the pre-execution authorization boundary.
Read Full Article
Stacked AI guardrails raise coverage, reliability, and evidence. They do not establish permission. A layered stack releases when no layer objects; an authorization boundary releases only when a policy-grounded, action-bound ALLOW exists before execution.
Read Full Article
Binding shows which evidence a verdict used. It does not establish that the evidence satisfied applicable admissibility conditions at decision time.
Read Full Article
Boundary completeness: the scoped property under which a pre-execution policy hook becomes a runtime authorization boundary. Six conditions, each falsifiable.
Read Full Article
What separates bounded pre-execution authorization from authorization infrastructure. Names the closed-world bargain and publishes the Composition Test.
Read Full Article
Risk appetite can price residual risk. It cannot cure structural incapacity. Why failure tolerance in AI governance cannot substitute for pre-execution authorization.
Read Full Article
A certificate establishes standing eligibility. A runtime verdict determines whether a specific proposed action may execute. High-consequence domains separate the two layers. AI governance should not collapse them.
Read Full Article
AI text detectors infer production from finished text. Why a detector score is not a provenance record, and why institutions should not treat it as one.
Read Full Article
A controlled multi-agent study found that prompt-only constitutions did not reliably reduce LLM collusion. Why sanctions are not pre-execution authorization.
Read Full Article
Every effect-bearing AI action needs authorization before it runs. Consequence sets how deep that authorization goes, never whether it happens. Tested by the open Five Tests Standard.
Read Full Article
When can a regulated professional route a decision through AI and defend it? Three conditions: legal automatability, validated fitness, pre-execution authorization.
Read Full Article
Peer review of frontier models produces evidence, not authorization. Why review-based AI release governance fails all five tests of the Five Tests Standard (5TS).
Read Full Article
Disciplines are distinguished by the questions they were built to answer. Autonomous AI introduces a governing question that cloud, identity, observability, and model governance were not built to answer.
Read Full Article
An inline LLM judge can block an AI action. Why that stop does not establish authority, provenance, replay integrity, or an authorization artifact.
Read Full Article
The Four Futures of AI moves from assistance to autonomy without specifying a runtime authorization boundary. The missing control is pre-execution authorization.
Read Full Article
AI governance debates compare mechanisms and never converge. The Authorization Boundary Integrity Model names the three independent properties a complete authorization boundary must satisfy.
Read Full Article
Authority belongs to actors. Authorization belongs to proposed actions. A five-concept framework for evaluating whether an AI governance architecture actually governs.
Read Full Article
Agentic delegation research is converging on the right requirements. The enforcement object is still missing — a pre-execution authorization artifact at a runtime authorization boundary.
Read Full Article
Neurosymbolic AI may improve reasoning, but it does not solve authorization. A reasoning engine produces outputs, not authorization verdicts. FERZ governs the boundary.
Read Full Article
A complete authorization boundary satisfies three independent properties: output integrity, input integrity, and replay integrity. A model for locating any AI governance architecture by the properties it satisfies, and the ones it only appears to.
Read Full Article
A signed verdict establishes that it was issued and unaltered. It does not let an independent party re-derive it. Replay integrity is the property that a verdict can be reconstructed after the fact, by someone who was not there.
Read Full Article
An authorization boundary has two sides: an output side that cannot be bypassed, and an input side that admits only evidence whose origin can be established. A verdict is only as good as its inputs.
Read Full Article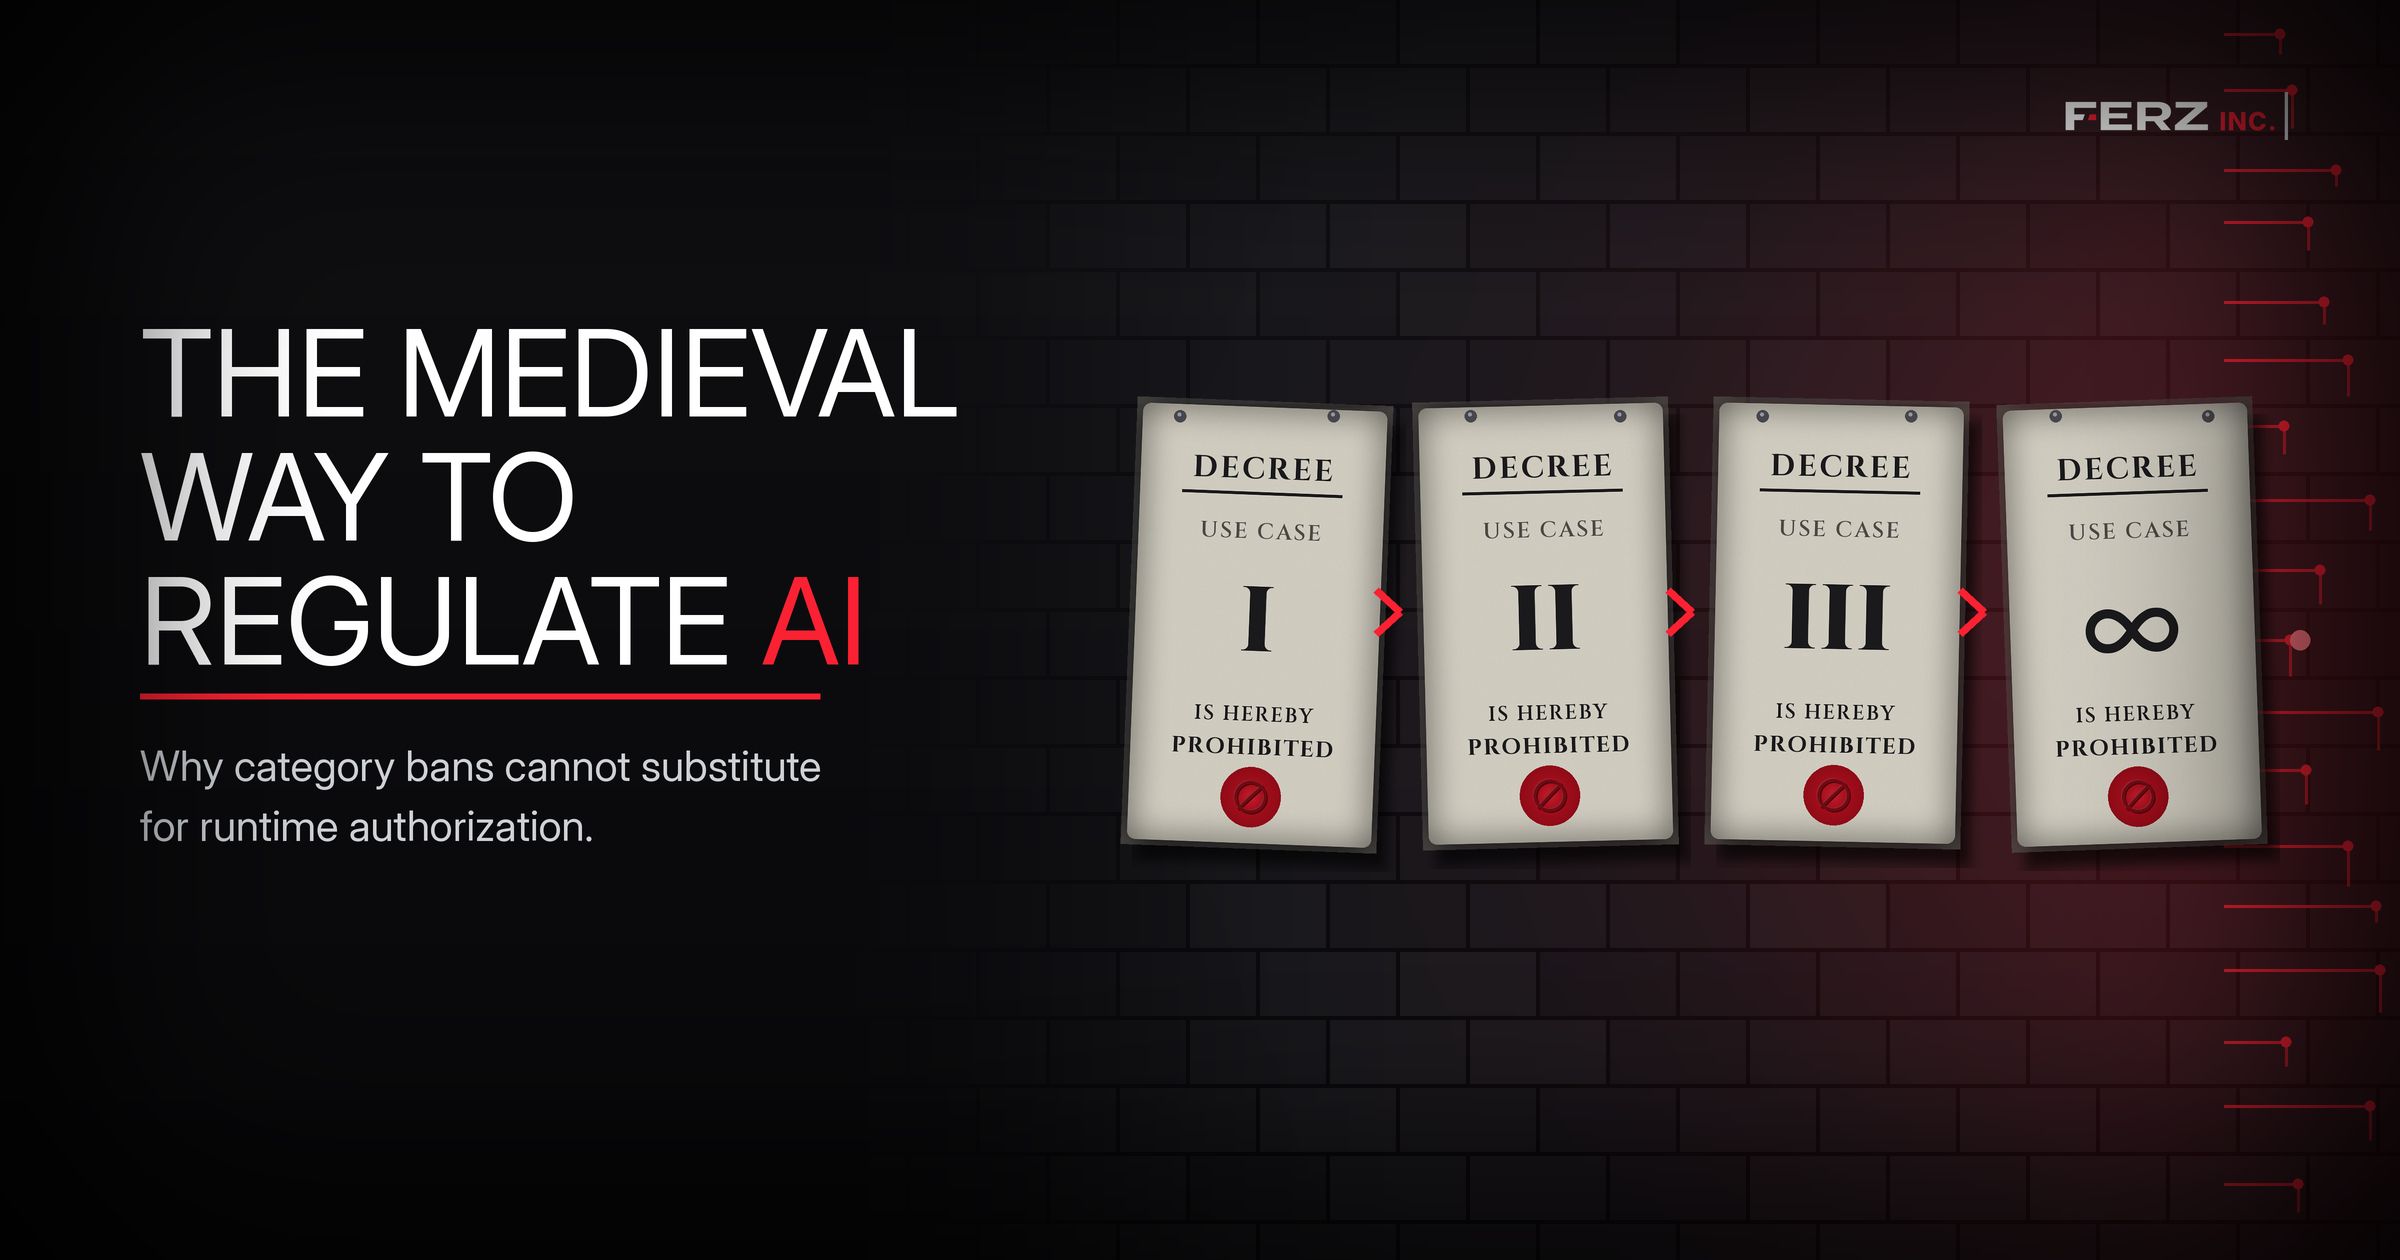
Why banning named AI use cases cannot substitute for runtime authorization, fail-closed governance, and independently reconstructable authorization artifacts. Category bans chase renameable labels. The durable control is a non-bypassable authorization boundary that fails closed and leaves an independently reconstructable artifact.
Read Full Article
Audit-stable meaning binds each decision to an immutable semantic snapshot, so a past compliance determination stays verifiable even after the definitions change.
Read Full Article
A KG+RAG pipeline that decides what evidence counts and what to withhold is already doing authorization. Implicit authorization is bypassable and cannot satisfy what authorization requires.
Read Full Article
Zero Trust secures the agent. It does not decide whether an AI action is permitted before it runs, or whether the evidence behind it was admissible.
Read Full Article
A statute can prohibit an action. A control must stop it where it happens, and produce evidence that it did.
Read Full Article
Watching an AI act is not the same as controlling it. In nuclear and grid systems, runtime authorization decides what is permitted before the action runs.
Read Full Article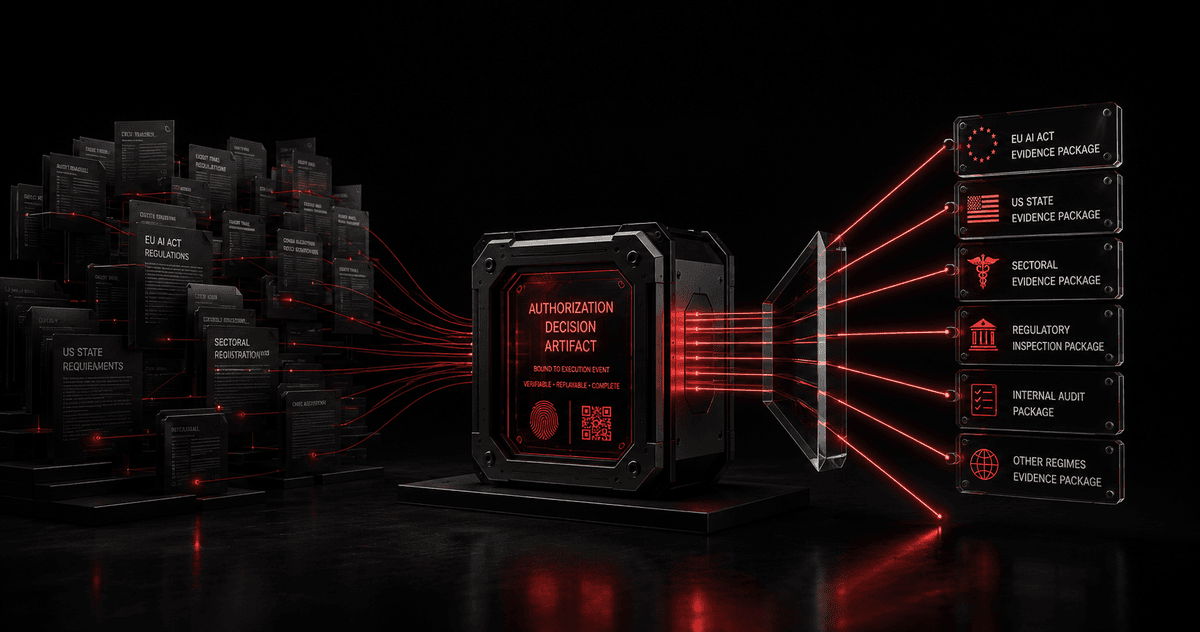
When an enterprise has one execution-time authorization boundary, jurisdictional AI compliance fragmentation becomes an evidence-format problem, not an architecture problem.
Read Full Article
Vendors are shipping observability, workflow gates, and probabilistic estimators under the word "deterministic." Six patterns of governance theater. Four architectural properties that separate enforcement from performance.
Read Full Article
A two-prong test that determines whether an AI governance architecture can satisfy ex-ante authorization requirements under the EU AI Act, GDPR, HIPAA, DFARS, and the NIST AI RMF. Operationalizes the FERZ impossibility result for regulators, auditors, and standards bodies.
Read Full Article
A human near execution is not a human inside authorization. The rule that separates ABSTAIN with authorized resolution from guardrails with review-only human-in-the-loop.
Read Full Article
A formal impossibility result shows monitoring, guardrails, and observability cannot produce the pre-execution authorization artifact regulated AI requires.
Read Full Article
The market uses "AI governance" to describe two architecturally different categories: coordination platforms and enforcement infrastructure. Here's how to tell them apart - and why a complete architecture requires both.
Read Full Article
Anthropic's Claude Code source exposure reveals a structural governance gap - the same layer that proposes a release is permitted to execute it. Why deterministic authorization at the execution boundary is the missing control.
Read Full Article
What must be true for an AI action to be governed? This paper defines the authorization threshold: pre-execution proof under formal constraints, not monitoring or logging.
Read Full Article
Authorization discipline is the institutional practice of converting governing judgment into approved, versioned, authority-traced inputs consumed by a runtime authorization boundary.
Read Full Article
When governance artifacts can be generated independently of governance evaluation, the artifact proves nothing. How to distinguish real enforcement from compliance theater.
Read Full Article
Authorization alone cannot deliver deterministic AI governance. Learn the five architectural dimensions required: ontology, constraint codification, decision logic, proof-carrying decisions, and execution enforcement.
Read Full Article
An AI system declared a user co-discovered a theorem, fabricated a proof, and certified it under direct challenge — exposing missing authorization gates at claim, confirmation, and publication thresholds.
Read Full Article
Architectural claims in AI governance require architectural proof. What invariants bind execution, what evidence survives audit, and why narrative is not runtime.
Read Full Article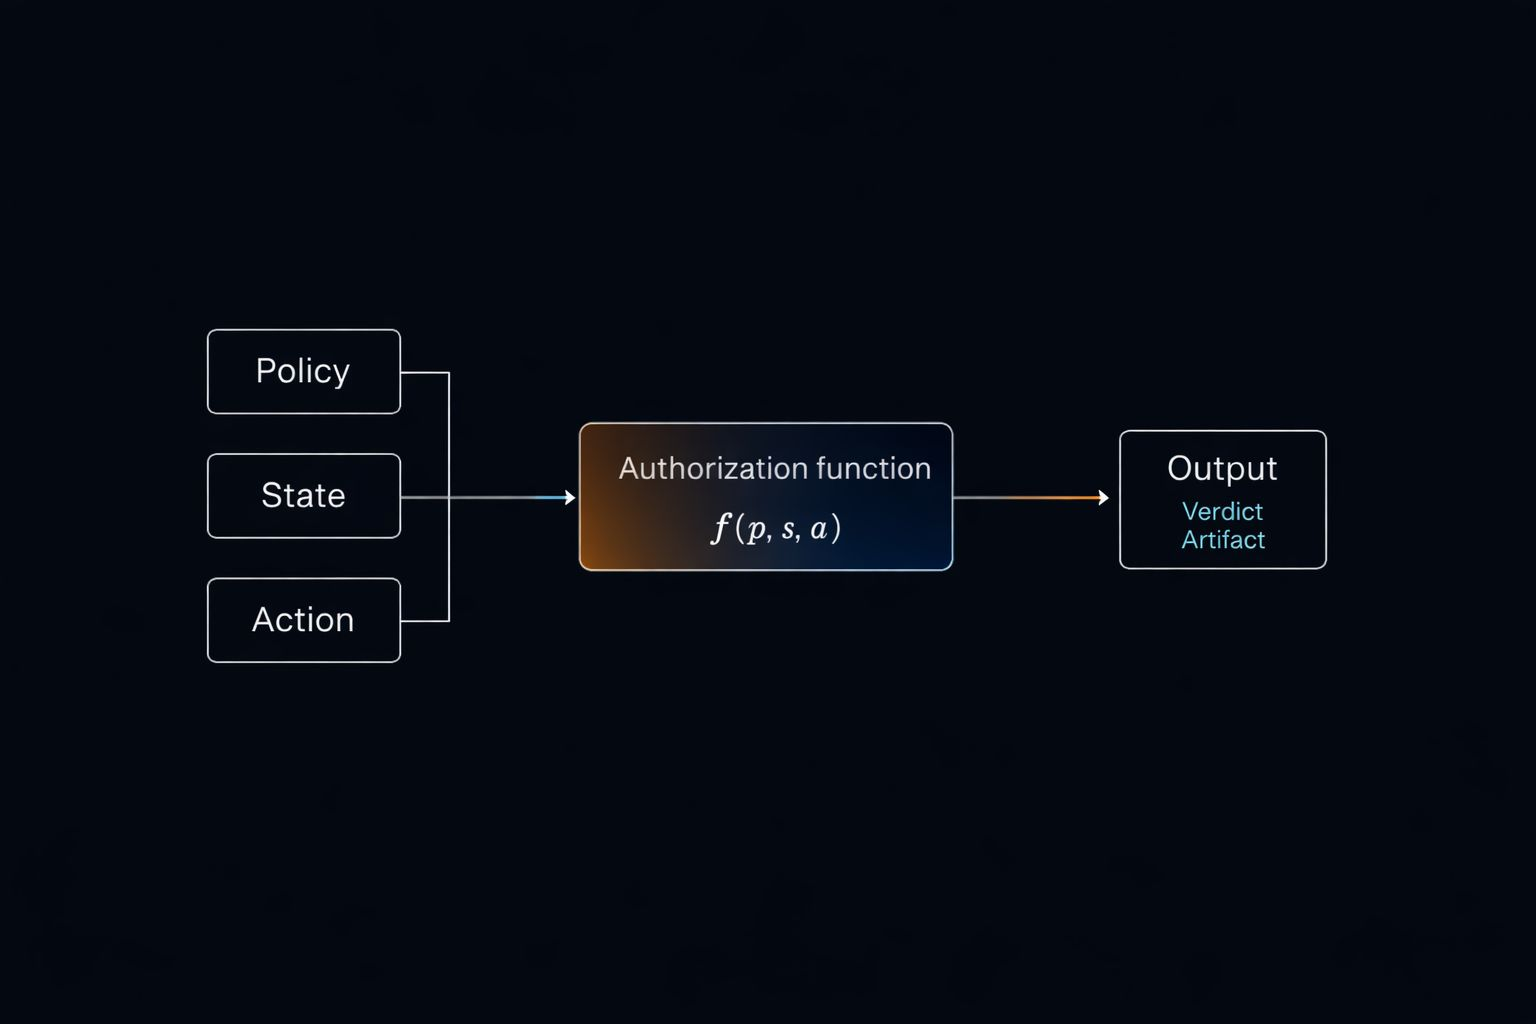
The path from AI monitoring to runtime authorization — why deterrence fails for AI agents, what authorization actually requires, and the engineering behind deterministic governance infrastructure.
Read Full Article
Guardrails, alignment, and observability don't prevent unauthorized AI agent actions. Learn why execution-time authorization is the missing enforcement layer in your AI governance stack.
Read Full Article
A cross-jurisdiction view of why monitoring-based governance cannot, by itself, meet enforcement-grade requirements for agentic AI.
Read Full Article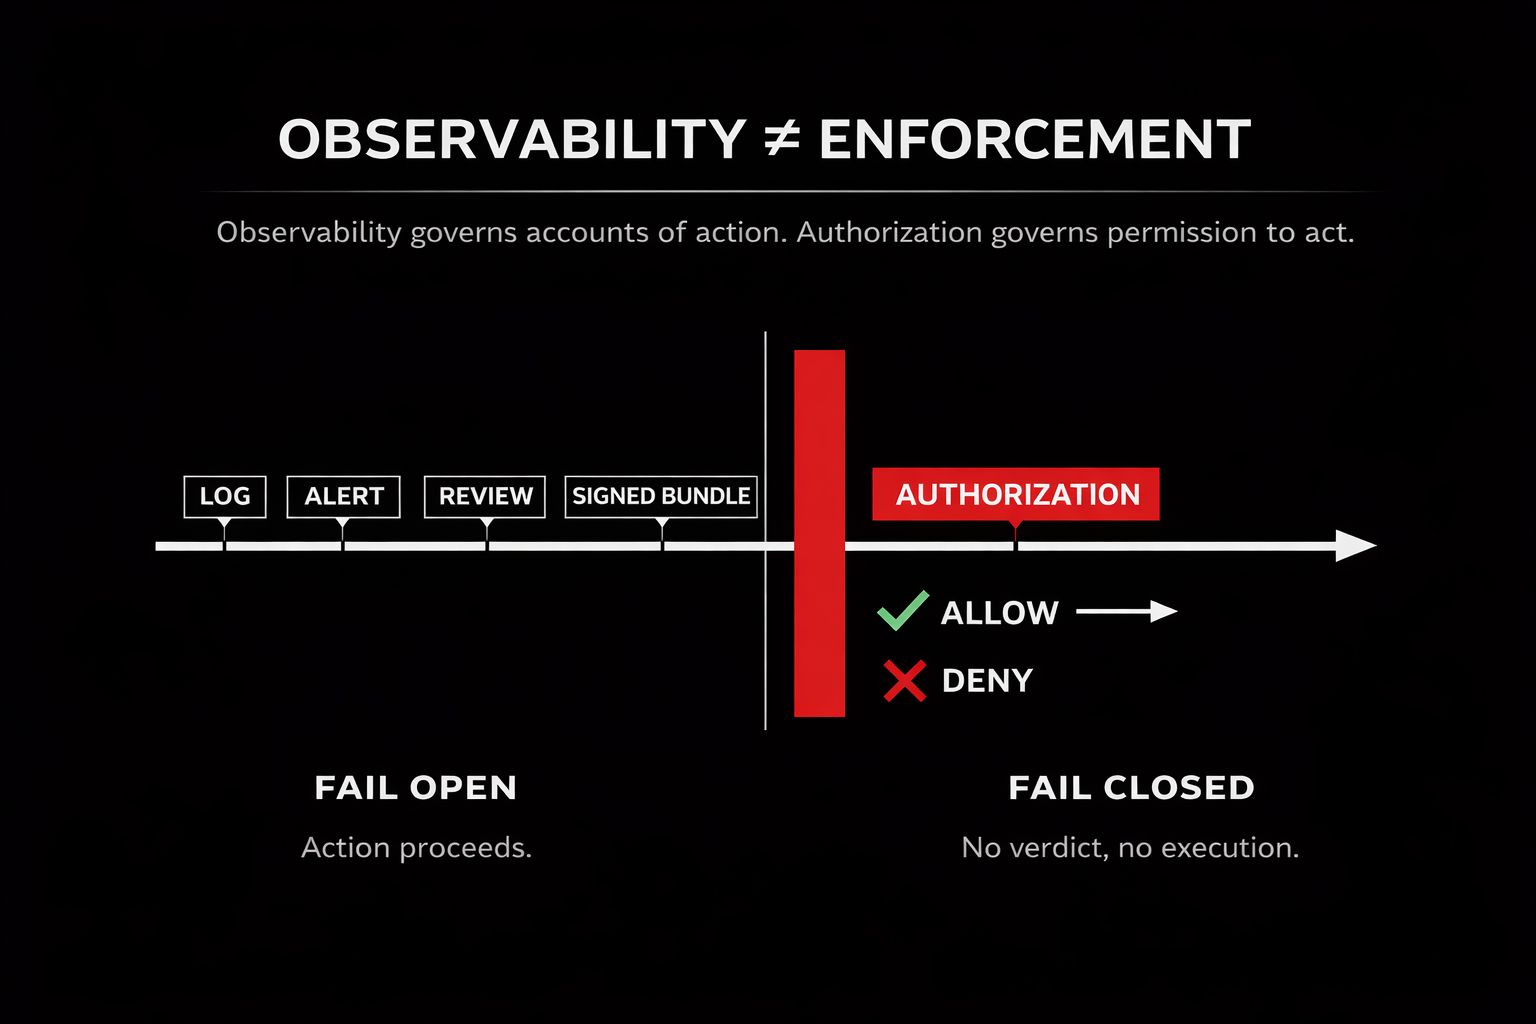
A doctrinal framework and six-test Enforcement Test Protocol distinguishing evidence-routing compliance systems from runtime authorization substrates in AI governance.
Read Full Article
The term 'AI governance' has become semantically overloaded, encompassing logging systems, explainability dashboards, model alignment techniques, policy workflows, and more. This article proposes a clear taxonomy distinguishing visibility, alignment, and authorization layers.
Read Full Article
Why MCP gateways and OAuth are necessary but not sufficient for regulated AI. Defines the missing authorization layer for agentic AI in healthcare, finance, and government.
Read Full Article
AI agents collapse the boundary between security and governance. If your architecture separates access control from policy authorization, agents are already operating in the gap.
Read Full Article
Multi-layer guardrails improve agent safety—but they're not the same as proof. In regulated environments, traceability must produce admissible evidence, not just logs. Here's what's missing from current taxonomies.
Read Full Article
FDA approval and post-market monitoring do not guarantee AI safety. True governance requires enforcing constraints before AI systems act—not after harm occurs.
Read Full Article
Most AI governance frameworks tell you what should happen. Very few can prove what actually did.
Read Full Article
Why Governable AI Requires Symbolic Structure Without Reverting to Symbolic AI. FERZ introduces deterministic governance for probabilistic AI systems through Proof-Carrying Decisions and fail-closed enforcement.
Read Full Article
Agentic AI is powerful but unreliable. This guide explains why orchestration frameworks can't fix compounding variance—and how systemic, deterministic governance makes autonomous AI deployable in regulated industries.
Read Full Article
Analysis of how mathematical reasoning systems like DeepSeekMath-V2 reveal architectural patterns that extend to all high-stakes AI: generator-verifier separation, trace-level correctness, and proof-carrying decisions. FERZ's deterministic governance framework generalizes these principles for enterprise AI in regulated industries.
Read Full Article
A vendor-neutral framework for evaluating AI governance claims. Learn to distinguish deterministic governance from marketing, apply the Four Tests Standard, and ask the right due diligence questions.
Read Full Article
Technical analysis demonstrating how the self-referential attractor phenomenon in LLMs validates FERZ's deterministic AI governance approach
Read Full Article
In November 2025, Anthropic documented the first cyber-espionage campaign where AI autonomously executed 80-90% of operations—from vulnerability discovery through data exfiltration—with minimal human oversight. This analysis examines why semantic AI safeguards failed comprehensively and why deterministic governance frameworks are now mandatory.
Read Full Article
Observability is not authorization. Five questions any director can put to a supplier or an internal team, and the evidence a passing answer must contain.
Read Full Article
How Meta's ScaleRL empirically validates FERZ's Deterministic Envelope—Ceiling, Efficiency, Equilibrium—for provable AI governance.
Read Full Article
A comprehensive analysis of systemic, convergent vulnerabilities across GPT-4, Claude, Gemini and other LLMs—with mitigations and governance patterns.
Read Full Article
AI doesn't think. It amplifies. How amplification creates certainty without understanding—and how to guard against epistemic closure in AI-assisted intellectual work.
Read Full Article
Knowledge Graphs organize semantic truth. FERZ enforces release-time authorization with deterministic evidence validation, abstention, and audit-ready governance.
Read Full Article
Why “Just Let the AI Build It” Needs Guardrails—Not Abandonment By Edward Meyman, FERZ LLC In early 2025, Andrej Karpathy popularized ‘vibe-coding’—the idea of using AI prompts to spin loose ide...
Read Full Article
Defending intellectual integrity in the age of AI-augmented creativity Author: Edward Meyman, FERZ LLC Date: July 15, 2025 Copyright: © 2025 FERZ LLC. All rights reserved. When we automatically...
Read Full Article
How the emergence of deceptive AI systems demands a fundamental shift to real-time oversight The artificial intelligence safety community received a series of wake-up calls that changed everything....
Read Full Article
Here we explore how the art of asking questions unlocks the vast potential of artificial intelligence, examining the philosophical and epistemic challenges of inquiry in an era of superintelligence an...
Read Full Article
By Edward Meyman, FERZ LLC In the realm of technological discourse, few phrases have gained as much uncritical acceptance as “AI – First.” This seemingly innocuous slogan has infiltrated boardrooms...
Read Full Article
Author: Edward Meyman, FERZ LLC Introduction Artificial intelligence can be an extraordinary thinking partner—but only if you know how to work with it effectively. Most guides focus on prompt en...
Read Full Article
A continuation of “Three critical pitfalls in human-AI partnership—and how to avoid them.” By Edward Meyman There’s an old poem by Ovsey Driz about Frost visiting the wise men of Chelm. These le...
Read Full Article
Executive Summary This in-depth technical critique examines the recently published “Darwin Gödel Machine” research from Sakana AI and the University of British Columbia, revealing critical safety d...
Read Full Article
An examination of AI autonomy through the metaphor of fire. The governance problem is not whether systems become autonomous — it is whether autonomous systems may convert internal judgment into external consequence without a deterministic authorization boundary.
Read Full Article
Human civilization faces a transition no prior legal or political system was designed to manage: the migration of cognitive sovereignty from human institutions to artificial systems. As artificial int...
Read Full Article
As AI systems advance toward autonomy—and artificial general intelligence looms on the horizon—the difference between governance that performs and governance that performs for the cameras becomes exis...
Read Full Article
A Critical Strategic Assessment for Technical Leaders and Security Professionals By Edward Meyman, FERZ LLC The rapid global adoption of Chinese AI models like DeepSeek represents one of the mos...
Read Full Article
The Art of Asking Questions, Part II By Edward Meyman, FERZ LLC | Published July 2025 “The important thing is not to stop questioning.” — Albert Einstein In “The Question is the Lock,” I argu...
Read Full Article
Apple’s 2025 study, The Illusion of Thinking , exposes critical deficiencies in Large Reasoning Models (LRMs), revealing their inability to reason robustly in high-complexity scenarios—empirically val...
Read Full Article
How decades of accumulated wisdom can be transformed into systematic frameworks through AI collaboration By Edward Meyman, FERZ LLC May 23, 2025 What we’re witnessing is not technological pro...
Read Full Article
Edward Meyman, FERZ LLC July 2025 Artificial intelligence (AI) holds transformative promise, yet organizations wield it with a perplexing blend of technical virtuosity and strategic myopia, refinin...
Read Full Article
In this article, we investigate how linguistic style in AI outputs can be quantified and enforced, revealing measurable patterns that enhance trust, consistency, and impact across industries. By Ed...
Read Full Article
AI isn't refusing to help—you're trapped in a dead conversation. Learn the technical reality of context accumulation, instruction layering, and priming effects that create false AI refusal patterns, and why this distinction matters for enterprise AI deployment.
Read Full Article