The Governance Gap: Why Process Controls Don't Prevent Runtime Failures
There's a scene playing out in boardrooms across every regulated industry. An executive presents the company's AI governance framework: documented policies, defined roles, risk assessments, training records, change management procedures. The slides look impressive. The audit committee nods approvingly.
Meanwhile, somewhere in the organization's infrastructure, an AI system is making decisions. Thousands of them. Every hour. And not one of those decisions carries proof that the governance framework was actually applied at the moment of execution.
This isn't a failure of intention. It's a failure of architecture.
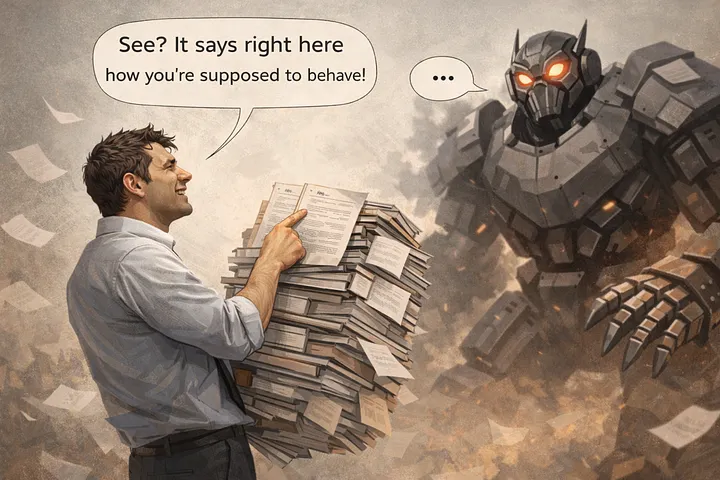
Explaining rules to a system unable (or unwilling) to enforce them isn't governance.
Two Kinds of Governance
The AI governance conversation has largely focused on what we might call process governance: the management systems, documentation, and organizational structures that define how AI should be developed, deployed, and monitored. This is the domain of ISO/IEC 42001, the EU AI Act's management system requirements, and most enterprise AI governance frameworks.
Process governance answers questions like: Do we have an AI policy? Have we assessed risks? Are roles and responsibilities defined? Is there a review cadence? Do we maintain training records?
These are important questions. Having documented processes is better than having no processes. But process governance operates at the organizational layer. It governs the humans who govern the AI, not the AI's decisions themselves.
Runtime governance is different. It operates at the execution layer, at the actual moment when an AI system produces an output that becomes an action, a decision, or a commitment. Runtime governance answers a fundamentally different question: Can we prove that this specific decision, made at this specific moment, complied with policy?
The distinction matters because process governance and runtime governance solve different problems. Process governance ensures an organization has the capability to govern AI. Runtime governance ensures that capability was actually exercised for any given decision.
The Evidence Problem
Consider what happens when something goes wrong: a biased hiring decision, an incorrect medical recommendation, a regulatory violation. The lawyers arrive. The regulators ask questions. The auditors demand evidence.
Under a process governance model, the organization can demonstrate that a policy existed prohibiting the problematic behavior, that employees were trained on the policy, that a risk assessment identified the category of risk, that a review process was in place, and that documentation was maintained.
What the organization typically cannot demonstrate is whether this specific decision was evaluated against policy before it was made, whether the system was authorized to make this decision at this moment, what inputs and reasoning led to this output, whether anyone could have stopped it before it became consequential, or whether an independent party could reproduce the decision trail.
In other words: the organization can prove it intended to govern AI decisions. It cannot prove it actually governed this decision.
This is not a hypothetical gap. It's the standard operating condition for most enterprise AI deployments today.
Why Logs Aren't Proof
The reflexive response is usually: "But we have logs."
Logs are valuable. They record that something happened. But logs are not governance evidence.
Logs are observational, not authoritative. A log entry says "decision X was made at time T." It doesn't say "decision X was authorized by policy Y, which was in effect at time T, signed by authority Z, and here's the cryptographic proof."
Logs can be incomplete, altered, or lost. In any serious dispute (litigation, regulatory investigation, breach response) the integrity of logs becomes a central question. Were they tampered with? Are they complete? Can we trust the timestamps?
Logs don't enable replay. If a regulator asks "how did you arrive at this decision?", a log entry typically can't answer that question. You can see that a decision was made, but you can't reconstruct why from the log alone.
Logs don't prove policy was applied. Logging that a model returned output X is different from proving that output X passed through a policy evaluation gate before it was released into the world.
And here's the critical point: logs don't constitute enforcement. If your governance architecture observes decisions and flags violations after execution, it is not governance, no matter how sophisticated the dashboard. A system that identifies a policy violation after the decision has already been made, the action already taken, the output already delivered to the customer, has not governed anything. It has documented a failure. Governance means the violation couldn't happen in the first place because the gate wouldn't open.
The distinction between logging and governance is the distinction between a security camera and a locked door. The camera records what happened. The door actually prevents unauthorized access. Most AI governance frameworks have plenty of cameras. Very few have doors.
The categorical boundary is simple: if the control runs after the output is emitted, it's monitoring, not governance. Monitoring tells you what happened. Governance determines what can happen. No amount of monitoring sophistication changes which side of that line you're on. Even sub-second detection is still post-execution if the output has already crossed the boundary into a customer workflow.
The Anatomy of Runtime Governance
What would it take to actually govern AI decisions at runtime? Not just document intentions, but enforce constraints and produce evidence?
Four capabilities are essential.
Pre-execution authorization. Before a decision becomes consequential, it must pass through a gate. The gate evaluates the decision against applicable policy. If the policy check fails, the decision doesn't proceed. This is fail-closed behavior: the default is denial, not approval.
Identified authority. Someone (or some system) must sign off on the policy before execution begins. This isn't a vague "management approved the AI strategy." It's a cryptographically verifiable attestation that a specific policy was in effect, authorized by a specific party, during a specific time window.
Reproducible evidence. After the fact, an independent party should be able to verify that the decision complied with policy. This means either replaying the exact inputs and outputs (state replay) or re-evaluating the decision against the same policy gates (protocol replay). The evidence must be self-contained: a proof-carrying decision (a signed envelope containing policy hash, authority attestation, inputs, and replay instructions) that includes everything needed to verify it.
Escalation paths. When decisions fall outside policy bounds, there must be a defined route for human review. Escalation isn't optional; it's structurally required. The system knows the difference between "approved," "denied," and "requires human judgment."
These four tests — pre-execution authorization (Stop), identified authority (Ownership), reproducible evidence (Replay), escalation paths (Escalation) — form the minimum bar for verifiable AI governance. They're not about making AI "safe" in some abstract sense. They're about creating the evidentiary basis for accountability.
This Is Not a Maturity Gap
Here's what most organizations get wrong: they treat runtime governance as an upgrade to their existing architecture. Better monitoring. Improved logging. More sophisticated dashboards.
Become a member
It's not. This is a category error.
Most AI governance platforms are structurally incapable of producing proof objects. They observe decisions after they're made. They aggregate logs. They surface anomalies. They generate reports. All of that happens after the decision has already become consequential.
Fail-closed execution, where a decision cannot proceed without passing through an authorization gate, requires a fundamentally different architecture. You cannot retrofit a locked door onto a system designed as a hallway.
Most vendors cannot provide this because their products were designed around observability, not enforcement. Most enterprise architectures cannot support this because they were built for throughput, not authorization. The gap isn't about maturity or investment. It's about whether the foundational architecture produces proof or just records observations.
This is why the market is full of "AI governance" solutions that are actually monitoring tools with governance branding. They can tell you what happened. They cannot prove what was authorized.
The Audit Reality
Let's return to the boardroom. The executive is presenting the AI governance framework. Now imagine the auditor asks a different question:
"Pick any AI decision your organization made last Tuesday. Show me the cryptographic proof that it was authorized, the policy that applied, and how I can independently verify that the decision complied."
If your answer is "we'll pull logs and investigate," you don't have governance evidence. You have incident response.
Under a process governance model, this question is unanswerable. Not because the organization is negligent, but because the architecture doesn't produce this kind of evidence.
Under a runtime governance model, this is exactly the artifact the system generates, for every decision, automatically, as a byproduct of normal operation.
The difference isn't philosophical. It's structural. Either your architecture produces proof, or it doesn't.
What Process Governance Actually Is
Let's be precise about what process governance accomplishes. ISO/IEC 42001 certification means an organization has documented policies, defined roles, and review cadences. That's real. It's better than nothing.
But in regulated or high-liability contexts, process governance without runtime enforcement isn't governance. It's compliance signaling.
Worse: it can actively increase liability. An organization that has documented policies but cannot prove enforcement has created a paper trail demonstrating it knew what should happen and still cannot show it made it happen. That's not a defense. It's an admission.
The uncomfortable truth is that process governance frameworks create the appearance of control. They satisfy procurement checklists. They look good in board presentations. They may even satisfy auditors who don't know what questions to ask.
But when something goes wrong, when a decision creates harm and lawyers start asking for evidence, process documentation becomes exhibit A in the case against you. "We had a policy" is not a defense when the follow-up question is "show me it was enforced" and you can't.
Process governance can certify that governance exists as paperwork. Runtime governance is what makes it exist as a property of execution.
The Coming Reckoning
Regulatory pressure is accelerating. The EU AI Act introduces obligations for high-risk AI systems that go beyond documentation, including requirements for traceability, technical documentation of decision-making, and the ability to demonstrate compliance. US federal agencies are beginning to require AI governance attestations from contractors. Sector-specific regulators in healthcare, finance, and beyond are developing AI-specific requirements.
These regulatory frameworks are still maturing, but the direction is clear: documentation of intent is giving way to demonstration of compliance. Regulators want proof, not promises.
Organizations that build runtime governance capabilities now will be positioned to meet these requirements. Organizations that rely solely on process governance will find themselves retrofitting, expensively and urgently, when the regulatory reality catches up.
More pragmatically: the first major AI liability case that turns on "can you prove this decision was governed?" will reshape the entire conversation overnight. The question isn't whether that case is coming. It's which organization will be the defendant.
What This Means for Practitioners
If you're responsible for AI governance in your organization, here's the uncomfortable question to sit with:
Can we prove, not assert, not document, not claim, that any specific AI decision we made last month was actually governed at the moment it was made?
If the answer is no, you have a process governance framework. It's better than nothing. But it's not runtime governance, and it won't produce the evidence you'll need when something goes wrong.
The path forward involves recognizing the category error. Most organizations conflate "we have policies" with "we enforce policies." They're not the same thing. One is documentation. The other is architecture. No amount of investment in the first produces the second.
It means demanding execution-layer evidence. When evaluating AI governance solutions, ask: does this produce proof, or just logs? Can an independent party replay a decision? Is enforcement fail-closed or fail-open? If the vendor's answer involves dashboards and anomaly detection, you're looking at monitoring, not governance.
It means building toward verifiability. Runtime governance isn't a product you buy and install. It's an architectural capability. It requires rethinking how AI decisions are made, authorized, and recorded. This is structural work, not procurement.
And it means starting with high-risk use cases. You don't need runtime governance for every AI application. Start with the decisions that create liability: regulated domains, consequential actions, customer-facing systems. The cost of retrofitting is highest where the stakes are highest.
The Bottom Line
There's a conceptual confusion at the heart of most AI governance discussions: the belief that documenting what should happen is equivalent to ensuring it does happen.
Process governance tells you what the rules are. Runtime governance proves the rules were followed.
Documentation explains intent. It doesn't enforce behavior.
Most organizations have the first. Very few have the second. The gap between them is where liability lives.
This article is part of an ongoing series on deterministic AI governance. The Four Tests Standard (4TS) provides an open specification for verifiable AI governance, including schemas, test vectors, and a reference implementation.